How to Use REA to Reverse-Engineer Apps with AI Agents
Learn what REA does, how its MCP and CLI workflows inspect apps and binaries, how to set it up, and what its evidence can—and cannot—prove.
Engineering · 5 min read · Kriyvo journal
In this article
Introduction
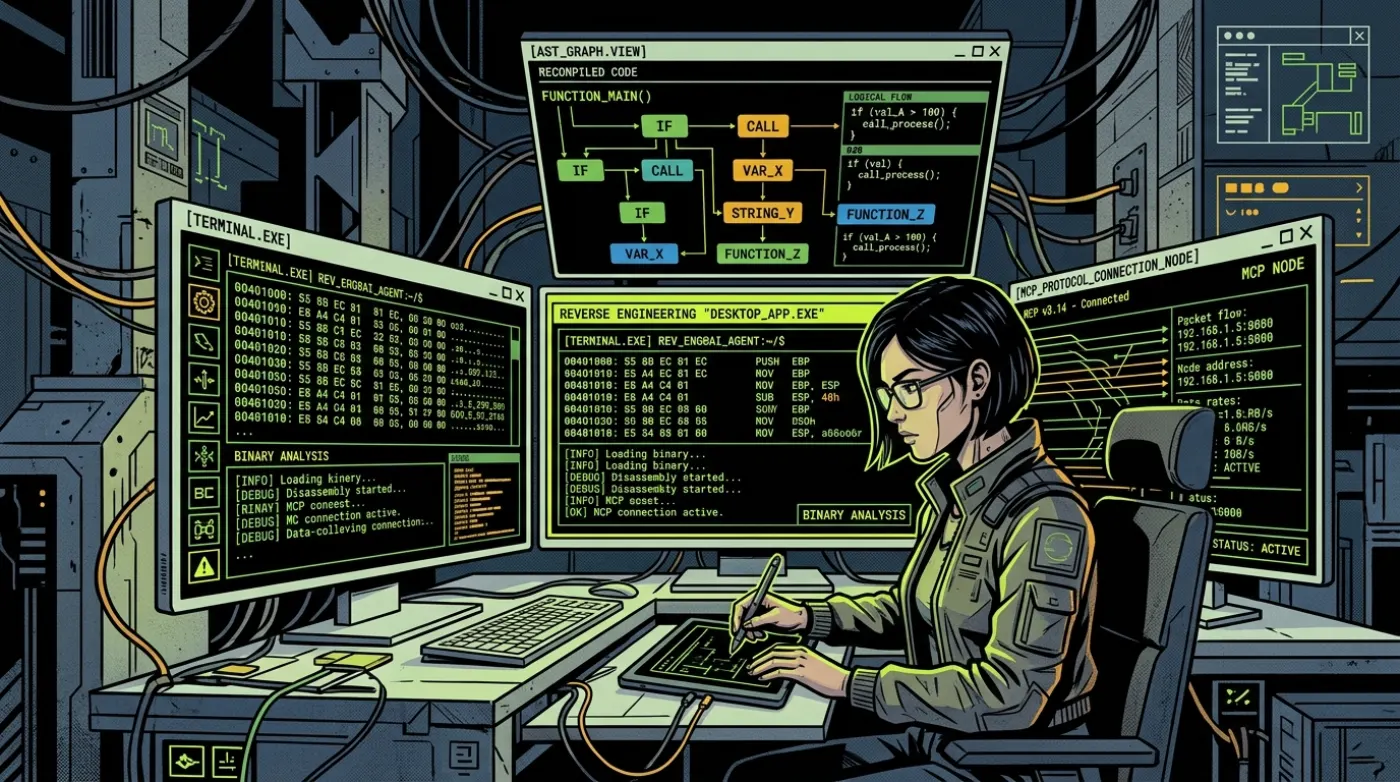
Reverse engineering architecture: binary AST parsing, MCP bridge & automated decompilation
The most relevant news articles and launch reviews grouped by what they help you understand.
Covers availability, pricing, industry use cases, and Google's competitive position.
Frames the release as Google's attempt to return to the leading edge of frontier AI and examines its claims against rival models.
Tests practical tasks involving website creation, videos, data analysis, and documents. The author reports useful outputs but also an unsupported claim in a launch summary, making this a relevant counterpoint to purely promotional coverage.
Real user discussions and community post titles comparing practical performance, benchmarks, and quota limitations.
The author tested Argon against Claude Opus 5.5 on a real feature for a production Python backend. A GPT-6 Astra judge scored the two plans 59/100 for Argon versus 77/100 for Opus 5.5. The author cautioned that more testing was needed and questioned context compaction speed.
The main community discussion is mixed. One commenter praised Argon's clear, logically structured answers and said they would use it for non-coding work. Others questioned its coding performance, total cost per task, and whether official benchmark wins translate into practical results.
An early Ultra subscriber described promising Blender 3D scripting and complex HTML results, comparing them favorably with Opus 5.5. Replies were more cautious, pointing to independent benchmark standings and average performance.
Reverse engineering has traditionally required specialized familiarity with disassemblers, hex editors, decompilers, and symbol tables. The open-source project REA (morluto/rea) bridges this gap by connecting autonomous coding agents—such as Claude Code, Codex, or custom agent harnesses—to static and dynamic software analysis tools via the Model Context Protocol (MCP).
Rather than forcing developers to manually navigate Ghidra, Hopper, or Node AST dumps, REA acts as an agent-connected toolkit. When paired with a coding assistant, an engineer can query how a local cache functions, inspect how an Electron app stores encrypted tokens, or extract undocumented network endpoints from a compiled binary.
Important reality check: REA is an evidence-oriented investigation toolkit—not an automated clone button. It does not magically recover original human-written source code, variable names, or internal architecture comments. This guide walks through its architecture, setup command, MCP configuration, and real-world boundaries.
What can REA actually inspect?
REA organizes its tooling around target types, selecting appropriate analyzers based on the file format and inspection objective:
- Native Binaries (Mach-O, ELF, PE): Inspects compiled C/C++, Rust, and Go binaries. Extracts string references, symbol tables, imported shared libraries, and calls decompilation engines like Ghidra or Hopper when installed.
- JavaScript & Electron Applications: Unpacks .asar archives, parses bundled webpack/vite artifacts, recovers obfuscated AST nodes, and traces IPC channel communications between main and renderer processes.
- .NET Assemblies & CIL: Analyzes intermediate bytecode, reconstructs type definitions, and inspects reflection manifests in desktop and enterprise tools.
- Web Applications & Network Behavior: Traces API requests, WebSocket frames, and serialized schema payloads to map external service contracts.
How REA executes an authorized reverse-engineering workflow
The developer prompts their coding agent (e.g. Claude Code) with a specific, bounded question—such as identifying an undocumented API endpoint or inspecting how local search indexes items in an Electron app.
Prerequisites & installation
REA requires a modern Node.js environment (v18+) and standard command-line developer utilities. To install REA globally and configure connected agents, run the official setup script:
Note: For native decompilation of Mach-O or ELF binaries, REA can optionally delegate to headless Ghidra (analyzeHeadless) or Hopper. If neither is installed, REA falls back to native disassembly routines (otool, objdump, nm, and strings).
Connecting REA to Claude Code via MCP
REA exposes a standard Model Context Protocol (MCP) server. To register REA inside Claude Code or Cursor, add the server entry to your MCP configuration file (claude.json or ~/.config/claude-code/config.json):
Once configured, restart your coding agent. Claude Code will automatically detect REA tools such as inspect_binary, extract_strings, unpack_asar, and decompile_function.
Practical demo: Inspecting an Electron app bundle
In an authorized security audit of an internal Electron desktop application, we tasked Claude Code with identifying how the app stores OAuth refresh tokens on disk.
1. Unpacking: Claude called unpack_asar on the target application package.
2. AST Parsing: REA extracted the bundled main.js and parsed IPC handlers registered via ipcMain.handle.
3. Evidence: REA surfaced a call to keytar.setPassword and identified the exact keychain service name used across macOS and Windows.
4. Synthesis: Rather than reading 50,000 lines of minified JavaScript, the developer received a 4-bullet executive summary citing file lines and exact method signatures.
What REA does NOT do: Essential boundaries
It is critical for engineering teams and security researchers to understand the limits of AI-assisted reverse engineering:
- Does not recover original source code: Variable names, comments, and high-level syntactic sugar stripped during compilation or minification cannot be perfectly restored.
- Does not guarantee a 1-click clone: REA produces technical evidence. Replicating proprietary logic or building an interoperable clean-room implementation still requires manual software engineering.
- Static analysis may miss dynamic execution: Code paths loaded dynamically via eval(), encrypted payloads, or remote webviews will not show up in purely static binary disassembly.
- Legal and authorization boundaries: Always ensure you possess explicit legal authorization or ownership over the target software before performing decompilation or reverse engineering.
REA vs traditional reverse-engineering tools
The table below illustrates how REA compares with established disassembly and decompilation software:
Need this built? LLM and AI agent development
Bounded AI applications and agents using Python, LangGraph, retrieval and controlled API integrations.
See the serviceWritten for the Kriyvo journal. Product claims reported by third-party sources are not independent Kriyvo AI benchmarks.